The art of Phishing Attacks

The art of Phishing Attacks.

Anonymous Hackers pose Assassination Threat to the President of the United States

Anonymous Hackers take AIM at the President of the United States.

Hundreds of Twitter Users Identified as Anonymous Hackers

Hundreds of Twitter Users Identified as Anonymous Hackers.

Is your money really safe?

With the threat of hackers targeting banks and showing no interest in protecting consumers, are banks safe?

Spies are watching your every move

People always talk about big brother spying on the populous, but hackers are doing most of the spying and using that information against you!

Showing posts with label #Anonymous. Show all posts

5/30/2015

New evidence of paid protesting


UPDATE: You can download all the screen shots including those not included here:


There has been a lot of talk lately about who's paying for protesters to go to various cities and protest events on the ground. the paper trail usually leads to big names like MORE, and George Soros. however something sparked my interest in the ability to buy violent protests in the street anywhere in the United States you wanted.

What I found even more disturbing was the fact that if it's that easy to shut down any intersection, or even an entire Interstate System, could this be exploited by our enemies like Iran, Russia, China, or even ISIS. Because the interstate system is designed to allow our military forces to quickly move from their bases to any city in the country, if you shut this down with citizens, the military will be less likely to force their way through the crowds, this at the very least creates a serious delay before help can arrive during an attack.

It seems logical that if you're the enemy and you want to cripple the ability for ground troops to respond quickly to an attack, you would also tie up all resources the police has available to a single location, then no one will be able to respond quickly enough for a terrorist attack on any building, airport, power station, etc.

These are all serious risks, and no one seems to be doing anything about exposing the movement for what it is. while this may not directly be an attack itself, it's showing our enemies how effective it is. there's a reason you can't shutdown roadways in countries like China or Russia, they view this as a weakness to respond to an attack.

We at Consternation Security have been working on tearing down the leadership of the opferguson movement since it was based on false facts and showed to be violent and mainly controlled from the outside. we decided to start with the most radical of them all, this was Bassem Masri, He was about to take a trip to Berkely California with 2 other streamers.

Proof of middle eastern influence 

Proof of American activism against the US Military

Our goal was to not only create a sense of paranoia during the entire trip, but also notify law enforcement in California, and Nevada to be on the look out for their vehicle. so on DEC 12TH, 2014, we published the license plate and vehicle information for what they were driving.

more on Bassem here


This allowed Law Enforcement to closely monitor their movements and activities state to state, and track where they were staying while in California. Next we moved on to what may have been the easiest person to break down. His nickname is VanMan and lives in California, he is part of the FTP crew, against both Police and Military, also against Israel. which is one reason we had no problem going for him. tearing down his psychological well being was done over a period of about two weeks utilizing many methods from in person psychological warfare to digital attacks. by creating a constant state of paranoia we were able to destroy his public image and made him a complete joke to the world who watched his streams.


Next we hit decided to see how willingly these protesters would go to a city and shutdown streets for whatever reason they are told to. so we contacted StackIzShort who has moved to the twitter handle Fergusonstream1 after having her main account suspended for making a death threat against iHazCandy with a picture of a gun. Because of that threat, we were relentless in tearing her down and everyone around her. after she reached a point where her entire life was turned upside down, she had no other options but to come work for us.
(StackIzShort has been restored as of Tuesday 02 June 2015 you can find her there)

We already knew she was hungry for money, after we setup a Honeypot to feel her out. after offering her a job to take a trip to Houston, Texas to protest Ted Cruz for being Canadian, she agreed for $1,000 a week plus travel expenses, which came out to be $150. we paid the travel expenses up front to to make it seem more realistic, and started the planning phase of the project.


I explained to her that the goal of the protest was to be anti-Canadian, and chant things like  "GO HOME CANADIANS". while she was a little resistant at first, she agreed to do it so long as she didn't have to publicly tweet out the racial chants against Canadians. we found it very interesting that someone involved with a movement who claims to be against racism, Black Lives Matter, was willing to utilize racist chants against the Congressman Ted Cruz.

Below you can follow along the conversation to see how we were able to use their greed for money as a reason to sell their soul to the devil and go against everything they claim to be about.

The Ferguson Stream Team.


Stacks, RAF, we could have left you stranded in Houston.
See how nice we really are?
You can reach ThatsRacistAF at 314-827-9937
She should rename her handle to IMRacistAF
Why you hate Canadians?

If you like our work and would like to help us continue to expose the truth behind the Anti-Police Movement spreading across our country like a fire, please consider donating to our cause at
http://gogetfunding.com/isis-reporting-center/

Social Engineering: @iHazcandy
Finances: @MeKissableMe


Operations are Sponsored by PatriotVPN


Questions or comments?
Message me on Twitter @iHazcandy
No permission is needed to share this information, People need to know the truth and what these people are really about.

Like what we've done here?
You can support our other project here:
http://gogetfunding.com/isis-reporting-center/

12/31/2013

Anonymous OpSafeWinter exposed as fraudulent


After several hours researching the so called operation safe winter being conducted by Anonymous I found several red flags. mainly wepay donation pages.


I also discovered an iconic image being shared with the claims that they helped this poor old man in the cold with fruit and money.

The truth? the image originally came from an article discussing homeless by choice, and the value of money. the man pictured from the OPSafeWinter accounts had nothing to do with them or their campaign to gain funds and support.


Since scamming and otherwise abusive behavior is taking place by people involved with this operation, including the campaign being used to spam the anti-government opNSA. I am exposing ip's of people involved, and supporting the opsafewinter campaign.

There are some bot's in the list, but that's to be expected when phishing.

First I wanted to test how effective the trap was, so i ran over to the main Anonops irc channel #Anonops. Sure enough, I got some hits, curious discovery was one IP was inside facebook's own corporate network. could this be facebook monitoring hacker activity? or has one of their servers/computers been compromised? Hard to say.

December 31, 2013: 199.59.161.30 <--- Bot
December 31, 2013: 31.151.158.2 <--- Human
December 31, 2013: 96.255.149.128 <--- Human
December 31, 2013: 81.157.105.93 <--- Human
December 31, 2013: 75.16.201.31 <--- Human
December 31, 2013: 173.252.74.119 <--- Facebook?!?
December 31, 2013: 67.81.217.135 <--- Human

Next I went over to cyber gorilla's IRC Network to further test things, but i found it to be mainly dead and just full of idling users despite all the advertising it's received in the last few weeks. All I got was some hits from their server bots that display the title of the url posted.

December 31, 2013: 5.9.108.74 <--- Bot

Since I've already exposed the site in this test, it was time to burn it down. I posted the link from the Anonrelations account on twitter and watched the hits and RT's. I'm not going to sift through the list and pick out the automated bots but the first 9 hit way too fast to be human.

December 31, 2013: 199.59.148.210 <-- Too fast to be human
December 31, 2013: 199.59.148.209 <-- Too fast to be human
December 31, 2013: 69.164.201.127 <-- Too fast to be human
December 31, 2013: 54.241.198.78   <-- Too fast to be human
December 31, 2013: 54.241.198.78   <-- Too fast to be human
December 31, 2013: 74.112.131.242 <-- Too fast to be human
December 31, 2013: 74.112.131.241 <-- Too fast to be human
December 31, 2013: 46.236.7.246     <-- Too fast to be human
December 31, 2013: 54.241.41.133   <-- Too fast to be human

The rest are anyone's guess. I was able to cross reference some of these with older logs, and they were in fact associated with several known anonymous members. so in that aspect, the honeypot was a success.

December 31, 2013: 65.52.244.38
December 31, 2013: 173.192.79.101
December 31, 2013: 46.236.24.48
December 31, 2013: 98.137.207.17
December 31, 2013: 54.196.145.175
December 31, 2013: 199.59.148.211
December 31, 2013: 37.59.16.156
December 31, 2013: 199.59.161.30
December 31, 2013: 54.224.152.41
December 31, 2013: 46.252.18.106
December 31, 2013: 46.246.92.155
December 31, 2013: 74.112.131.241
December 31, 2013: 23.227.176.35
December 31, 2013: 23.227.176.34
December 31, 2013: 23.227.176.35
December 31, 2013: 98.137.207.17
December 31, 2013: 46.236.26.102
December 31, 2013: 54.225.58.239
December 31, 2013: 130.155.204.198
December 31, 2013: 212.124.109.166
December 31, 2013: 74.96.97.57
December 31, 2013: 50.57.227.76
December 31, 2013: 74.112.131.242
December 31, 2013: 54.225.52.78
December 31, 2013: 66.249.74.72
December 31, 2013: 199.189.85.8
December 31, 2013: 205.188.94.164
December 31, 2013: 54.196.127.20

Now that things are broken down. lets take a look at the header data on a few of these, and that will give us a better indication of what's a bot, and who's human.

Anonops Bot.
199.59.161.30 - - [31/Dec/2013:13:19:03 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 59585 "-" "Mozilla/5.0 (Compatible; Supybot 0.83.4.1+gribble (2011-08-12T18:12:56-0400))"

Human
31.151.158.2 - - [31/Dec/2013:13:19:20 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11116 "-" "Mozilla/5.0 (Windows NT 6.1; WOW64; rv:26.0) Gecko/20100101 Firefox/26.0"

Human
96.255.149.128 - - [31/Dec/2013:13:19:21 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11116 "-" "Mozilla/5.0 (Windows NT 6.1; WOW64; rv:26.0) Gecko/20100101 Firefox/26.0"

Human
81.157.105.93 - - [31/Dec/2013:13:19:31 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11116 "-" "Mozilla/5.0 (Windows NT 6.3; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/31.0.1650.63 Safari/537.36"

Human
75.16.201.31 - - [31/Dec/2013:13:20:33 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11116 "-" "Mozilla/5.0 (Windows NT 6.1; WOW64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/31.0.1650.63 Safari/537.36"

Interesting Facebook hit from inside anonops.
173.252.74.119 - - [31/Dec/2013:13:22:08 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 206 11165 "-" "facebookexternalhit/1.1 (+http://www.facebook.com/externalhit_uatext.php)"

Human
67.81.217.135 - - [31/Dec/2013:13:28:13 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11116 "-" "Mozilla/5.0 (Windows NT 6.3; WOW64; rv:26.0) Gecko/20100101 Firefox/26.0"

Cyber Gorilla IRC Bot
5.9.108.74 - - [31/Dec/2013:13:58:49 +1100] "HEAD /story/24320782/anonymous-helps-the-homeless-in-houston-tx HTTP/1.1" 301 285 "-" "Mozilla/5.0 (X11; Linux i686; rv:2.0.1) Gecko/20100101 Firefox/4.0.1"

Interesting. amazon IP. automated i'm sure.
54.241.198.78 - - [31/Dec/2013:14:04:48 +1100] "HEAD /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 227 "-" "Google-HTTP-Java-Client/1.17.0-rc (gzip)"

Human
65.52.244.38 - - [31/Dec/2013:14:04:50 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11114 "-" "Mozilla/5.0 (compatible; MSIE 10.0; Windows NT 6.1; Trident/6.0)"

Appears human but tried to snag robots.txt. not familiar with flipboard.
54.196.145.175 - - [31/Dec/2013:14:05:46 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx HTTP/1.1" 301 597 "-" "Mozilla/5.0 (Macintosh; U; Intel Mac OS X 10.6; en-US; rv:1.9.2) Gecko/20100115 Firefox/3.6 (FlipboardProxy/1.1; +http://flipboard.com/browserproxy)"

Hi twitter.
199.59.148.211 - - [31/Dec/2013:14:06:55 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11114 "-" "Twitterbot/1.0"

Aww how cute. someone was going to post my article as fact.. you know. cause the internet said it was real.
37.59.16.156 - - [31/Dec/2013:14:07:18 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11170 "-" "Mozilla/5.0 (compatible; PaperLiBot/2.1; http://support.paper.li/entries/20023257-what-is-paper-li)"

Human
46.246.92.155 - - [31/Dec/2013:14:09:22 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11170 "-" "Mozilla/5.0 (Windows; U; Windows NT 6.0; ru; rv:1.8.1.20) Gecko/20081217 Firefox/2.0.0.20"

Interesting
98.137.207.17 - - [31/Dec/2013:14:13:56 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 59613 "-" "NING/1.0"

Human - Ipad news reader
54.225.58.239 - - [31/Dec/2013:14:14:09 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11133 "-" "Mozilla/5.0 (Macintosh; Intel Mac OS X 10_6_6) AppleWebKit/534.24 (KHTML, like Gecko) Contact: feedback@getprismatic.com"

Not sure.
130.155.204.198 - - [31/Dec/2013:14:15:10 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 58824 "-" "Java/1.6.0_27"

Another NING
212.124.109.166 - - [31/Dec/2013:14:20:39 +1100] "HEAD /story/24320782/anonymous-helps-the-homeless-in-houston-tx HTTP/1.1" 301 366 "-" "NING/1.0"

Human
74.96.97.57 - - [31/Dec/2013:14:20:42 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11169 "http://t.co/WlGhlJdTYz" "Mozilla/5.0 (Windows NT 6.0; rv:26.0) Gecko/20100101 Firefox/26.0"

web proxy I think
50.57.227.76 - - [31/Dec/2013:14:20:42 +1100] "HEAD /story/24320782/anonymous-helps-the-homeless-in-houston-tx HTTP/1.1" 301 285 "-" "EventMachine HttpClient"

Human
54.225.52.78 - - [31/Dec/2013:14:21:00 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 11170 "-" "Mozilla/5.0 (Windows; U; Windows NT 5.1; en-US; rv:1.9.0.8) Gecko/2008091620 Firefox/3.0.2"

Human
205.188.94.164 - - [31/Dec/2013:14:21:20 +1100] "GET /story/24320782/anonymous-helps-the-homeless-in-houston-tx/ HTTP/1.1" 200 59613 "-" "Jakarta Commons-HttpClient/3.1"

I'll look deeper into the logs when I get time, I do see that injection was successful on most occasions.


4/06/2012

TeaMpoison TeamDX PonyCr3w IP HISTORY

I'm tired of the games. this leak is an act of revenge for the lawless acts against my country, it's people, and it's government. We will not tolerate you anons being more oppressive than the oppressor. you can not lead by terrorizing the citizens of the world. This is simply my way of saying "f**k you"

Congratulations, on leaving cookie crumbs all over the interwebs.

Below are some IP addresses we have a record of.

#TeaMpoison

I've been watching you kids play #hacktheplanet for some time.
Now you will pay for committing acts of war against my country!
Now you can pay for threatening COPS who protect the PEOPLE!
Now you can pay for stealing consumer credit card data and sharing it!


46.4.7.198 - static.198.7.4.46.clients.your-server.de - AS24940 HETZNER-AS Hetzner Online AG RZ
173.197.85.109 173.197.64.0/18   AS20001 (not registered)
66.232.107.140 - 66.232.96.0/19 - AS29802
46.4.7.198 - static.198.7.4.46.clients.your-server.de - AS24940 - HETZNER-AS Hetzner Online AG RZ
98.151.28.201 - 98.151.0.0/18 RR-Route - AS20001 (not announced)
64.120.47.217 - 64.120.47.0/24 Route for NTG Chicago - AS15003 (not announced)
178.73.220.45 - AS42708 - PORTLANE Network www.portlane.com
186.22.218.187 -  186.22.0.0/15 - AS27747 (not registered)
64.178.181.157 - 64.178.176.0/20 - AS2828 (not registered)
95.90.43.80 - 95-90-43-80-dynip.superkabel.de - AS31334
KABELDEUTSCHLAND-AS Kabel Deutschland Breitband Service GmbH


3/21/2012

True story about the CubeCart Hack

For those of you following the CubeCart Hack that has left roughly 64,000 ecommerce businesses open to full database leaks, including personal details like credit card data.

It was not my intention to publish intimate the details of this case to the world as the truth will very likely create ripples through the shopping cart vendor CubeCart. We have made multiple requests to contact us regarding this issue, all of which had been received, but not replied to.

Rather than allow a company lie to their customers about the privacy of their data, we feel that the truth is the number one priority for any business dealing in sotware that holds consumer data.

The founder of CubeCart made a public statment on their company forums

"Just after Christmas, a script kiddie hacker managed to get a malicious file on our server from a security hole in our bug tracker. They then attempted to blackmail us in the usual low life way these people do. However we refused and quickly patched all the servers software and tightened our server security settings locking them out by closing any back door access they created. We were not aware of any breech of data until now and it appears that they have data up to the first few days of January 2012.

The hacker was furious that we didn't pay them and it looks like he/she managed to steal some data from the license system database from our company server and has irresponsibly posted this information online. To add insult to injury they are twisting the facts in an attempt to scare our customers and impact our business.

Please note that;
- the hacker stole data from OUR database. They have no means or method to access any part of your stores data at all.
- most importantly we do NOT store any credit card data on our servers.
- all software license keys remain in the hands of their original owners. No 3rd party is able to unlock or reset them so they have no control or power over your storewhatsoever.
- 64,000 shopping carts are NOT vulnerable. The article title is incredibly misleading and there is no reason to be alarmed as they do not have access to your stores database.
- our server is continually scanned by McAfee Secure for vulnerabilities and we do our very best to keep all software secure and up-to-date... however keeping a server totally bullet proof is never 100% possible and from time to time companies including high profile household names such as Sony have suffered similar exploits.

The only thing we can do is to sincerely apologise and continue and to review our security policies.
"


They claim that they were originally hacked Christmas of 2011, and blackmailed by the hacker, but failed to warn their customers of their data being compromised. They also claim the data we have obtained was dated 2012, which would make this the 2nd hack, one that they were not aware of.

They make mention of the hacker irresponsibly posted the information online, this is in reference to a now removed link to our website. a false accusation that we are the hacker only proving they are even more clueless about what really has happed than we thought.

They claim that the hacker stole data from only the cubecart company database, we have reason to suggest otherwise. but we will get to that later in this article.

They claim that they do not store credit card data on their servers,
no? then what is this?


"they have no control or power over your storewhatsoever." "64,000 shopping carts are NOT vulnerable"

False. Anonymous Hackers have a new ZeroDay attack they can use against CubeCart to gain full Database Access using what is called SQLi, They can even use google to locate roughly 64,000 websites running your software that the vulnribility currently works on and has been verified by highly skilled security professionals.

We find your remarks to be slanderous, and a down right lie to your customers. if you contacted us rather than avoiding the issue, you would have learned this information before your customers did.


How did we learn of this massive security breech of a leading ecommerce software solution?

We have previously investigated the hacker that tried to blackmail your company, and we have information on who he is, and even his IP address right now, but i guess you're not interested in that. right?
This was submitted to us by the hacker that molested your database.

One thing we know for sure, is he does not stop at one database, and he is all about automation. this means he most likely already has all 64,000 databases sitting on his servers while he buys bulk cheetos off ebay.


Also I love how you try and place blame on McAfee, You are the effing software developer, it was your code that got 64,000 of your customers owned. don't try to spread the blame. because all blame is on you.

Next time, just email us, and we won't have to bash you in a public forum like you did to us.

There is a ton of data to add to this, documented proof, names, hackers involved, groups, etc, but I think we have invested enough time and energy into a worthless cause of defending ourselves against a company that lies to their customers.

Cheers.

3/20/2012

Anonymous Hackers turn Remote Viewers into Weapons


Anonymous Hackers are having a difficult time working alone after the recent FBI raid that left core members behind bars. most are confused as to what direction they should go, who they should attack, and who will teach them the skills to gain access to systems with secure passwords.

After many ideas were passed around, a hacker that assisted wikileaks who goes by the name as b1gmonieZ came up with a unique solution to the problem. he suggested that they utilize social networking sites like twitter to seek out remote viewers.

Most people may not be aware what a remote viewer is, and those who have heard about this supernatural ability only turn their noses up at it. regardless if you believe in remote viewing, it is apparent that the United States Government takes it seriously.

In 1979 the Army's Intelligence and Security Command was ordered to develop a program utilizing remote viewers and in 1995 the CIA took over the project. There have been several operations that have been funded recently, including Schnabel in 1997, Smith in 2005, and in 2001 Atwater.

We have to wonder what the capabilities of Anonymous Hackers could be if they have the ability to use psychic powers to see into secret databases at top secret government facilities and National Security contractors.


The most troubling thought in a Hacker actually seeing what you see, not even super secure picture password solutions provided by Tricerion are safe from a Remote Viewer.

(yes this conversation really took place) where? anonops IRC

3/04/2012

Anonymous Hackers Discuss total Satellite Takeover


Anonymous Hackers discussed what to do with information obtained from NASA computer systems after they were able to gain access to sensitive information. the hackers now have the ability to access communication systems that control most satellite systems for broadcast media, weather, and military equipment.

Some ideas were shuffled around as to crash them all into the lower earth atmosphere and let them burn up, other ideas were to ram them into each other to create a spectacle that the world will be able to gaze up at the sky and see explosions above their heads.

Regardless of the method of destruction, the idea is all the same. show the world that Anonymous hackers have the ability to shutdown the entire world in a matter of minutes, and even launch satellite based nuclear missiles at government targets world wide.

Anonymous could succeed at such a bold attack against the Corporate world if protocols are not put into action to destroy every byte of information related to their movement, and everyone involved should be silenced to prevent the spread of the radical ideology anonymous stands for.

Who's to say they will stop at the satellites, what if they decide to fire the International Space station's engines and force it plummeting into the earth.

If the rich people around the world are unable to watch their Big Brother, Marry some rich guy, and shows making money off humiliation of would-be American Idols, maybe they would be more likely to get in the streets and protest the end to government.

This trend of Anonymous members integrating themselves into Occupy Wall street/your town movements is a dangerous move that could lead millions of Americans to be misdirected into violence creating riots and burning commercial property to the ground. this has already been experienced in California with a serious of fires. death by fire is the way they envision the end of modern society.

There have been rumors that the Hackers behind the NASA security breach were also behind the giant fireball seen over the UK. they may be using the documents to destroy satellites used by major corporations and Governments.

On the other hand, I guess we all have the right to talk about and discuss what you want to. it just makes it difficult to know who is really going to do something, and who is just BSing.

3/01/2012

Operation Sticky Fingers takes down Anonymous Wannabe Hackers


How did we catch us some dirty would be hackers?

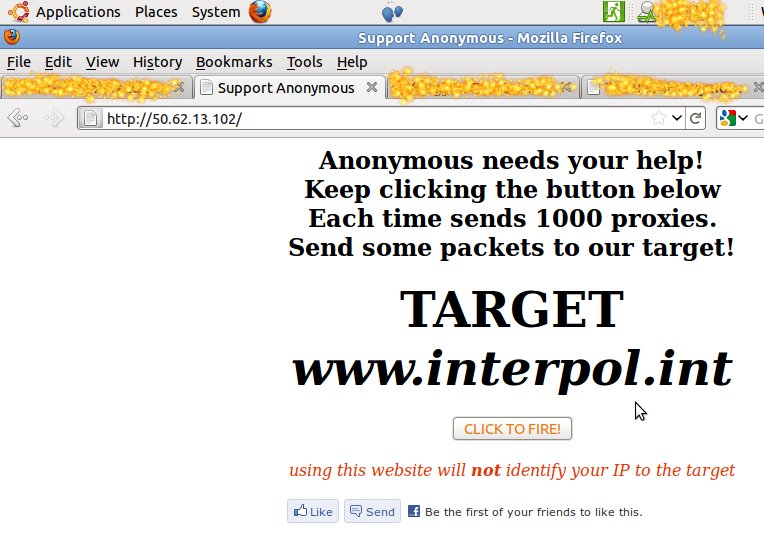
To catch a would be Anonymous Hacker is not very difficult. first you need an idea on what you are targeting. lets take the #interpol attack for example. we first setup a virtual linux server on the cloud that would be ready for the job of being a trap.  we went to work throwing together a very simple html page, with a php script that records the ip to file. nothing more, nothing less.

On our #stickyfingers operation we used the following script. we are firm beleivers that your source code should only include the task it is doing on the page it is doing it on. you're far less likely to create vulnerabilities that can open your server up to a number of problems.

Enjoy the code, hope you get a good laugh how simple it is. for the data it produced.

<html>
<head>
<meta content="text/html; charset=ISO-8859-1"
http-equiv="content-type">
<title>Support Anonymous</title>
</head>
<body>
<script src="//connect.facebook.net/en_US/all.js#xfbml=1"
id="facebook-jssdk"></script>
<div style="text-align: center;"><big><big><span
style="font-weight: bold;">Anonymous needs your help!</span><br
style="font-weight: bold;">
<span style="font-weight: bold;">Keep clicking the button below<br>Each time sends 1000 proxies.<br>
<?php

$logfile= '/var/www/html/thepot.html';
$IP = $_SERVER['REMOTE_ADDR'];
$logdetails=  date("F j, Y, g:i a O T") . ': ' .
'<a href=http://www.geobytes.com/IpLocator.htm?GetLocation&ipaddress='.$_SERVER['REMOTE_ADDR'].'>'
.$_SERVER['REMOTE_ADDR'].'</a>';
$fp = fopen($logfile, "a"); 
fwrite($fp, $logdetails);
fwrite($fp, "<br>");
fclose($fp); 

echo("Send some packets to our target!"); 

?>
</span></big></big><br>
<br>
<big><big><big><big><span style="font-weight: bold;">TARGET<br>
</span></big></big></big></big><cite><big><big><big><big><span
style="font-weight: bold;">www.</span><b style="font-weight: bold;">interpol</b><span
style="font-weight: bold;">.int</span></big></big></big></big><br>
<br>
<button style="color: rgb(233, 121, 17);" onfocus="f01" value="ftarget"
name="CLICK TO FIRE!" type="button">CLICK TO FIRE!</button>
<br>
<br>
<span style="color: rgb(228, 55, 9);">using this website will <span
style="font-weight: bold;">not</span> identify your IP to the target</span><br>
<br><div class="fb-like" data-href="http://yourhostname" data-send="true" data-width="450" data-show-faces="true"></div>
</cite></div>
<script>(function(d, s, id) {
var js, fjs = d.getElementsByTagName(s)[0];
if (d.getElementById(id)) return;
js = d.createElement(s); js.id = id;
js.src = "//connect.facebook.net/en_US/all.js#xfbml=1";
fjs.parentNode.insertBefore(js, fjs);
}(document, 'script', 'facebook-jssdk'));</script>


To break it down for you, the only important part of this code is the following part.

<?php

$logfile= '/var/www/html/thepot.html';
$IP = $_SERVER['REMOTE_ADDR'];
$logdetails=  date("F j, Y, g:i a O T") . ': ' .
'<a href=http://www.geobytes.com/IpLocator.htm?GetLocation&ipaddress='.$_SERVER['REMOTE_ADDR'].'>'
.$_SERVER['REMOTE_ADDR'].'</a>';
$fp = fopen($logfile, "a"); 
fwrite($fp, $logdetails);
fwrite($fp, "<br>");
fclose($fp); 

echo("Send some packets to our target!"); 

?>

Now all you have to do is create a file called thepot.html (or another name) and make it writable. 777.

Now just keep an eye on thepot file, and maybe even run the Linux command tail -f thepot.html to keep a scrolling eye on what's going on.

That's all there was to it. and it generated the huge list of ip's of Twitter users who are involved with Anonymous Hacking and DDOSing. 

trap IP log can be found here


2/29/2012

HAARP MAY HAVE ALREADY BEEN HACKED


Is there lightning, high winds, and maybe even a tornado at your front door right now? this could be the actions of Anonymous Hackers hacking the HAARP servers so they can gain control of the array. for obvious reasons most about this beautiful machine is classified, but you can still watch its wrath, and be prepared for trouble.


This radar image was from a couple days ago, notice the yellow area over the south east. 


below is the same radar image that has been shutdown by some god like force.


And here we have the current radar for the south east after there has been a tornado outbreak.


Watch this.